Radical Technologies
IT SECURITY
★★★★★
(2,095 ratings)  50,000+ Student

AWS Certified Security — Specialty

The AWS Certified Security – Specialty certification is a credential offered by Amazon Web Services (AWS) that validates an individual’s advanced expertise in securing AWS cloud environments. This certification is ideal for security professionals, AWS architects, and engineers who want to specialize in cloud security and are responsible for securing AWS workloads and infrastructure. It’s a valuable credential for those working extensively with AWS and focusing on security and compliance.

RT
Radical Technologies
50,000+ English 40 hours Weekdays / Weekends Classroom / Online / Corporate
Online / Classroom

AWS Certified Security — Specialty

IT Training Programme

Duration 40 hours
Batch Type Weekdays / Weekends
Mode of Training Classroom / Online / Corporate
Locations Pune, Bangalore, Kochi
Language English
Certification Globally Recognized
Call Now

100% placement assistance

Enquire Now

Get course fees, batch dates & a callback

We never share your details.

What you'll learn

Understand core concepts and architecture from the ground up
Get hands-on with the tools used by working professionals
Build real-world projects you can add to your portfolio
Learn industry best practices and coding standards
Practice with real datasets and real-world scenarios
Prepare for certification and technical interviews
Work on collaborative, team-based exercises
Apply performance tuning and optimization techniques
Understand how the technology fits into a larger ecosystem
Complete assignments reviewed by mentors

Programme Overview

6 sections covering the complete curriculum — a single, progressive learning arc.

40 hours
Training Duration
6
Core Modules
220
Total Lessons
4.7
Average Rating
50K+
Students Trained
01

Foundations & Core Concepts

Get hands-on with the fundamentals and architecture — the building blocks for everything that follows.

Fundamentals Architecture Setup
02

Hands-On Practical Training

Work through real exercises and assignments designed to mirror what you will do on the job.

Practicals Assignments Labs
03

Real-World Projects

Apply what you have learned to end-to-end projects that go straight into your portfolio.

Projects Portfolio Case Studies
04

Advanced Techniques

Go beyond the basics with advanced concepts, integrations and production-grade practices.

Advanced Integration Best Practices
05

Ecosystem Integration

Understand how this technology connects with the broader tools and platforms used in the industry.

Ecosystem Tools Platforms
06

Performance & Interview Prep

Master optimization techniques and prepare for the technical interview questions employers actually ask.

Optimization Interview Prep Certification

Who is this programme for?

Whether you're already writing code, working with data, or supporting applications today — this programme is built to take you into a IT SECURITY role.

Software Developers

Engineers who want to add this skill set to their toolkit

Analysts & Consultants

Professionals moving into a more technical, hands-on role

IT Professionals

System admins and support engineers upskilling into a new domain

Fresh Graduates

CS/IT graduates aiming for a job-ready technical role

Course Curriculum

6 sections  •  220 lessons  •  40 hours

01 Threat Detection and Incident Response

Design and implement an incident response plan.

– Knowledge of:
AWS best practices for incident response
Cloud incidents
Roles and responsibilities in the incident response plan
AWS Security Finding Format (ASFF)
– Skills in:
Implementing credential invalidation and rotation strategies in response to compromises (for example, by using AWS Identity and Access Management [IAM] and AWS Secrets Manager)
Isolating AWS resources
Designing and implementing playbooks and runbooks for responses to security incidents
Deploying security services (for example, AWS Security Hub, Amazon Macie, Amazon GuardDuty, Amazon Inspector, AWS Config, Amazon Detective, AWS Identity and Access Management Access Analyzer)
Configuring integrations with native AWS services and third-party services (for example, by using Amazon EventBridge and the ASFF)

Detect security threats and anomalies by using AWS services

– Knowledge of:
AWS managed security services that detect threats
Anomaly and correlation techniques to join data across services
Visualizations to identify anomalies
Strategies to centralize security findings
– Skills in:
Evaluating findings from security services (for example, GuardDuty, Security Hub, Macie, AWS Config, IAM Access Analyzer)
Searching and correlating security threats across AWS services (for example, by using Detective)
Performing queries to validate security events (for example, by using Amazon Athena)
Creating metric filters and dashboards to detect anomalous activity (for example, by using Amazon CloudWatch)

Respond to compromised resources and workloads.

– Knowledge of:
AWS Security Incident Response Guide
Resource isolation mechanisms
Techniques for root cause analysis
Data capture mechanisms
Log analysis for event validation
– Skills in:
Automating remediation by using AWS services (for example, AWS Lambda, AWS Step Functions, EventBridge, AWS Systems Manager runbooks, Security Hub, AWS Config)
Responding to compromised resources (for example, by isolating Amazon EC2 instances)
Investigating and analyzing to conduct root cause analysis (for example, by using Detective)
Capturing relevant forensics data from a compromised resource (for example, Amazon Elastic Block Store [Amazon EBS] volume snapshots, memory dump)
Querying logs in Amazon S3 for contextual information related to security events (for example, by using Athena)
Protecting and preserving forensic artifacts (for example, by using S3 Object Lock, isolated forensic accounts, S3 Lifecycle, and S3 replication)
Preparing services for incidents and recovering services after incidents
02 Security Logging and Monitoring

Design and implement monitoring and alerting to address security events.

– Knowledge of: 
AWS services that monitor events and provide alarms (for example, CloudWatch, EventBridge)
AWS services that automate alerting (for example, Lambda, Amazon Simple Notification Service [Amazon SNS], Security Hub)
Tools that monitor metrics and baselines (for example, GuardDuty, Systems Manager)
– Skills in:
Analyzing architectures to identify monitoring requirements and sources of data for security monitoring
Analyzing environments and workloads to determine monitoring requirements
Designing environment monitoring and workload monitoring based on business and security requirements
Setting up automated tools and scripts to perform regular audits (for example, by creating custom insights in Security Hub)
Defining the metrics and thresholds that generate alerts

Troubleshoot security monitoring and alerting.

– Knowledge of: 
Configuration of monitoring services (for example, Security Hub)
Relevant data that indicates security events
– Skills in:
Analyzing the service functionality, permissions, and configuration of resources after an event that did not provide visibility or alerting
Analyzing and remediating the configuration of a custom application that is not reporting its statistics
Evaluating logging and monitoring services for alignment with security requirements

Design and implement a logging solution.

– Knowledge of: 
AWS services and features that provide logging capabilities (for example, VPC Flow Logs, DNS logs, AWS CloudTrail, Amazon CloudWatch Logs)
Attributes of logging capabilities (for example, log levels, type, verbosity)
Log destinations and lifecycle management (for example, retention period)
– Skills in:
Configuring logging for services and applications
Identifying logging requirements and sources for log ingestion
Implementing log storage and lifecycle management according to AWS best practices and organizational requirements

Troubleshoot logging solutions.

– Knowledge of: 
Capabilities and use cases of AWS services that provide data sources (for example, log level, type, verbosity, cadence, timeliness, immutability)
AWS services and features that provide logging capabilities (for example, VPC Flow Logs, DNS logs, CloudTrail, CloudWatch Logs)
Access permissions that are necessary for logging
– Skills in:
Identifying misconfiguration and determining remediation steps for absent access permissions that are necessary for logging (for example, by managing read/write permissions, S3 bucket permissions, public access, and integrity)
Determining the cause of missing logs and performing remediation steps

Design a log analysis solution.

– Knowledge of: 
Services and tools to analyze captured logs (for example, Athena, CloudWatch Logs filter)
Log analysis features of AWS services (for example, CloudWatch Logs Insights, CloudTrail Insights, Security Hub insights)
Log format and components (for example, CloudTrail logs)
– Skills in:
Identifying patterns in logs to indicate anomalies and known threats
Normalizing, parsing, and correlating logs
03 Infrastructure Security

Design and implement security controls for edge services.

– Knowledge of: 
Security features on edge services (for example, AWS WAF, load balancers, Amazon Route 53, Amazon CloudFront, AWS Shield)
Common attacks, threats, and exploits (for example, Open Web Application Security Project [OWASP] Top 10, DDoS)
Layered web application architecture
– Skills in:
Defining edge security strategies for common use cases (for example, public website, serverless app, mobile app backend)
Selecting appropriate edge services based on anticipated threats and attacks (for example, OWASP Top 10, DDoS)
Selecting appropriate protections based on anticipated vulnerabilities and risks (for example, vulnerable software, applications, libraries)
Defining layers of defense by combining edge security services (for example, CloudFront with AWS WAF and load balancers)
Applying restrictions at the edge based on various criteria (for example, geography, geolocation, rate limit)
Activating logs, metrics, and monitoring around edge services to indicate attacks

Design and implement network security controls.

– Knowledge of: 
VPC security mechanisms (for example, security groups, network ACLs, AWS Network Firewall)
Inter-VPC connectivity (for example, AWS Transit Gateway, VPC endpoints)
Security telemetry sources (for example, Traffic Mirroring, VPC Flow Logs)
VPN technology, terminology, and usage
On-premises connectivity options (for example, AWS VPN, AWS Direct Connect)
– Skills in: 
Implementing network segmentation based on security requirements (for example, public subnets, private subnets, sensitive VPCs, on-premises connectivity)
Designing network controls to permit or prevent network traffic as required (for example, by using security groups, network ACLs, and Network Firewall)
Designing network flows to keep data off the public internet (for example, by using Transit Gateway, VPC endpoints, and Lambda in VPCs)
Determining which telemetry sources to monitor based on network design, threats, and attacks (for example, load balancer logs, VPC Flow Logs, Traffic Mirroring)
Determining redundancy and security workload requirements for communication between onpremises environments and the AWS Cloud (for example, by using AWS VPN, AWS VPN over Direct Connect, and MACsec)
Identifying and removing unnecessary network access
Managing network configurations as requirements change (for example, by using AWS Firewall Manager)

Design and implement security controls for compute workloads.

– Knowledge of: 
Provisioning and maintenance of EC2 instances (for example, patching, inspecting, creation of snapshots and AMIs, use of EC2 Image Builder)
IAM instance roles and IAM service roles
Services that scan for vulnerabilities in compute workloads (for example, Amazon Inspector, Amazon Elastic Container Registry [Amazon ECR])
Host-based security (for example, firewalls, hardening)
– Skills in:
Creating hardened EC2 AMIs
Applying instance roles and service roles as appropriate to authorize compute workloads
Scanning EC2 instances and container images for known vulnerabilities
Applying patches across a fleet of EC2 instances or container images
Activating host-based security mechanisms (for example, host-based firewalls)
Analyzing Amazon Inspector findings and determining appropriate mitigation techniques
Passing secrets and credentials securely to compute workloads

Troubleshoot network security.

– Knowledge of:
How to analyze reachability (for example, by using VPC Reachability Analyzer and Amazon Inspector)
Fundamental TCP/IP networking concepts (for example, UDP compared with TCP, ports, Open Systems Interconnection [OSI] model, network operating system utilities)
How to read relevant log sources (for example, Route 53 logs, AWS WAF logs, VPC Flow Logs)
– Skills in:
Identifying, interpreting, and prioritizing problems in network connectivity (for example, by using Amazon Inspector Network Reachability)
Determining solutions to produce desired network behavior
Analyzing log sources to identify problems
Capturing traffic samples for problem analysis (for example, by using Traffic Mirroring)
04 Identity and Access Management

Design, implement, and troubleshoot authentication for AWS resources.

– Knowledge of: 
Methods and services for creating and managing identities (for example, federation, identity providers, AWS IAM Identity Center [AWS Single Sign-On], Amazon Cognito)
Long-term and temporary credentialing mechanisms
How to troubleshoot authentication issues (for example, by using CloudTrail, IAM Access Advisor, and IAM policy simulator)
– Skills in:
Establishing identity through an authentication system, based on requirements
Setting up multi-factor authentication (MFA)
Determining when to use AWS Security Token Service (AWS STS) to issue temporary credentials

Design, implement, and troubleshoot authorization for AWS resources.

– Knowledge of: 
Different IAM policies (for example, managed policies, inline policies, identity-based policies, resource-based policies, session control policies)
Components and impact of a policy (for example, Principal, Action, Resource, Condition)
How to troubleshoot authorization issues (for example, by using CloudTrail, IAM Access Advisor, and IAM policy simulator)
– Skills in:
Constructing attribute-based access control (ABAC) and role-based access control (RBAC) strategies
Evaluating IAM policy types for given requirements and workloads
Interpreting an IAM policy’s effect on environments and workloads
Applying the principle of least privilege across an environment
Enforcing proper separation of duties
Analyzing access or authorization errors to determine cause or effect
Investigating unintended permissions, authorization, or privileges granted to a resource, service, or entity
05 Data Protection

Design and implement controls that provide confidentiality and integrity for data in transit.

– Knowledge of:
TLS concepts
VPN concepts (for example, IPsec)
Secure remote access methods (for example, SSH, RDP over Systems Manager Session Manager)
Systems Manager Session Manager concepts
How TLS certificates work with various network services and resources (for example, CloudFront, load balancers)
– Skills in:
Designing secure connectivity between AWS and on-premises networks (for example, by using Direct Connect and VPN gateways)
Designing mechanisms to require encryption when connecting to resources (for example, Amazon RDS, Amazon Redshift, CloudFront, Amazon S3, Amazon DynamoDB, load balancers, Amazon Elastic File System [Amazon EFS], Amazon API Gateway)
Requiring TLS for AWS API calls (for example, with Amazon S3)
Designing mechanisms to forward traffic over secure connections (for example, by using Systems Manager and EC2 Instance Connect)
Designing cross-Region networking by using private VIFs and public VIFs

Design and implement controls that provide confidentiality and integrity for data at rest.

– Knowledge of:
Encryption technique selection (for example, client-side, server-side, symmetric, asymmetric)
Integrity-checking techniques (for example, hashing algorithms, digital signatures)
Resource policies (for example, for DynamoDB, Amazon S3, and AWS Key Management Service [AWS KMS])
IAM roles and policies
– Skills in:
Designing resource policies to restrict access to authorized users (for example, S3 bucket policies, DynamoDB policies)
Designing mechanisms to prevent unauthorized public access (for example, S3 Block Public Access, prevention of public snapshots and public AMIs)
Configuring services to activate encryption of data at rest (for example, Amazon S3, Amazon RDS, DynamoDB, Amazon Simple Queue Service [Amazon SQS], Amazon EBS, Amazon EFS)
Designing mechanisms to protect data integrity by preventing modifications (for example, by using S3 Object Lock, KMS key policies, S3 Glacier Vault Lock, and AWS Backup Vault Lock)
Designing encryption at rest by using AWS CloudHSM for relational databases (for example, Amazon RDS, RDS Custom, databases on EC2 instances)
Choosing encryption techniques based on business requirements

Design and implement controls to manage the lifecycle of data at rest.

– Knowledge of:
Lifecycle policies
Data retention standards
– Skills in:
Designing S3 Lifecycle mechanisms to retain data for required retention periods (for example, S3 Object Lock, S3 Glacier Vault Lock, S3 Lifecycle policy)
Designing automatic lifecycle management for AWS services and resources (for example, Amazon S3, EBS volume snapshots, RDS volume snapshots, AMIs, container images, CloudWatch log groups, Amazon Data Lifecycle Manager [Amazon DLM])
Establishing schedules and retention for AWS Backup across AWS services

Design and implement controls to protect credentials, secrets, and cryptographic key materials.

– Knowledge of:
Secrets Manager
Systems Manager Parameter Store
Usage and management of symmetric keys and asymmetric keys (for example, AWS KMS)
– Skills in:
Designing management and rotation of secrets for workloads (for example, database access credentials, API keys, IAM access keys, AWS KMS customer managed keys)
Designing KMS key policies to limit key usage to authorized users
Establishing mechanisms to import and remove customer-provided key material
06 Management and Security Governance

Develop a strategy to centrally deploy and manage AWS accounts.

– Knowledge of: 
Multi-account strategies
Managed services that allow delegated administration
Policy-defined guardrails
Root account best practices
Cross-account roles
– Skills in:
Deploying and configuring AWS Organizations
Determining when and how to deploy AWS Control Tower (for example, which services must be deactivated for successful deployment)
Implementing SCPs as a technical solution to enforce a policy (for example, limitations on the use of a root account, implementation of guardrails in Control Tower)
Centrally managing security services and aggregating findings (for example, by using delegated administration and AWS Config aggregators)
Securing AWS account root user credentials

Implement a secure and consistent deployment strategy for cloud resources.

]
– Knowledge of: 
Deployment best practices with infrastructure as code (IaC) (for example, AWS CloudFormation template hardening and drift detection)
Best practices for tagging
Centralized management, deployment, and versioning of AWS services
Visibility and control over AWS infrastructure
– Skills in:
Using CloudFormation to deploy cloud resources consistently and securely
Implementing and enforcing multi-account tagging strategies
Configuring and deploying portfolios of approved AWS services (for example, by using AWS Service Catalog)
Organizing AWS resources into different groups for management
Deploying Firewall Manager to enforce policies
Securely sharing resources across AWS accounts (for example, by using AWS Resource Access Manager [AWS RAM])

Evaluate the compliance of AWS resources.

– Knowledge of: 
Data classification by using AWS services
How to assess, audit, and evaluate the configurations of AWS resources (for example, by using AWS Config)
– Skills in:
Identifying sensitive data by using Macie
Creating AWS Config rules for detection of noncompliant AWS resources
Collecting and organizing evidence by using Security Hub and AWS Audit Manager

Identify security gaps through architectural reviews and cost analysis.

– Knowledge of: 
AWS cost and usage for anomaly identification
Strategies to reduce attack surfaces
AWS Well-Architected Framework
– Skills in:
Identifying anomalies based on resource utilization and trends
Identifying unused resources by using AWS services and tools (for example, AWS Trusted Advisor, AWS Cost Explorer)
Using the AWS Well-Architected Tool to identify security gaps

Tools & Technologies

Every tool listed here is installed, configured and used in a hands-on lab session.

Core Tools

Hands-On Labs

Practical Environment

Industry-Standard Tools

Real-World Setup

Guided Exercises

Skill Building

Sample Datasets

Practice Material

Practice & Projects

Mini Projects

Applied Practice

Assignments

Mentor Reviewed

Doubt Sessions

Live Support

Career Readiness

Resume Building

Career Support

Mock Interviews

Interview Prep

Certification Prep

Global Recognition

Deployment & Delivery

Production Practices

Real-World Ready

Best Practices

Industry Standards

220+
Hands-On Lessons
6
Core Modules
40 hours
Training Duration
100%
Practical Training

You don't just learn AWS Certified Security — Specialty. You ship it.

Three major projects, each mirroring how production teams actually work — from guided foundations to a portfolio-ready capstone.

PROJECT // 01

Guided Foundation Project

Requirement Analysis

Guided Implementation

Mentor Review

Iteration

Foundation Beginner

Apply the fundamentals in a structured, mentor-reviewed project

Take the core concepts from the first half of the curriculum and apply them to a realistic scenario, with guidance and feedback from your mentor at every step.

Structured project brief
Step-by-step implementation
Mentor feedback and review
Documented outcome
Stack Core Concepts Best Practices
PROJECT // 02

Applied Practice Project

Scenario Design

Independent Build

Testing & Validation

Peer Review

Applied Intermediate

Build a more independent project mirroring real production scenarios

Work through a project that combines multiple concepts from the curriculum, closer to how work is actually structured on the job — less hand-holding, more ownership.

End-to-end implementation
Testing and validation
Documentation
Peer/mentor review
Stack Applied Skills Testing
PROJECT // 03

Capstone Project

Planning

End-to-End Build

Review & Refinement

Presentation

Capstone Advanced

Take a project from requirements to a polished, portfolio-ready deliverable

Your final project — plan, build, test and present a complete solution using everything covered in the curriculum, reviewed by mentors before you graduate.

Complete working solution
Presentation-ready documentation
Mentor sign-off
Portfolio-ready deliverable
Stack Full Curriculum Portfolio

All 3 projects go directly into your portfolio & resume — reviewed by mentors before you graduate.

See Sample Project Reports

Upcoming Batches

No upcoming batches scheduled right now. Enquire to get notified.

Why Radical Technologies

Live Online Training
  • Highly practical oriented training
  • Installation support on your system
  • 24/7 Email and Phone support
  • 100% Placement Assistance
  • Global Certification Preparation
  • Trainer-Student Interactive Portal
  • Assignments and Projects by Mentors
Live Classroom Training
  • Weekend / Weekdays / Morning / Evening batches
  • 80:20 Practical and Theory ratio
  • Real-life Case Studies
  • Easy make-up for missed sessions
  • PSI | Kryterion | Redhat Test Centers
  • Lifetime Video Classroom Access (coming soon)
  • Resume Prep and Mock Interviews
Self-Paced Training
  • Learn 300+ courses at your own time
  • 50,000+ Satisfied Learners
  • Course Completion Certificate
  • Practical Labs available
  • Mentor Support available
  • Doubt Clearing Session available
  • 10% Discounted Global Certification

Like the Curriculum? Let's Get Started

Join 50,000+ students already enrolled at Radical Technologies

Enroll Now

Global Certification

Radical Technologies is the leading IT certification institute in Pune, offering globally recognized certifications across various domains. With expert trainers and comprehensive materials, we ensure students gain in-depth knowledge and hands-on experience to excel in their careers. Our certification programs are tailored to meet industry standards — from cloud technologies to data science — empowering individuals to stay ahead in the ever-evolving tech landscape.
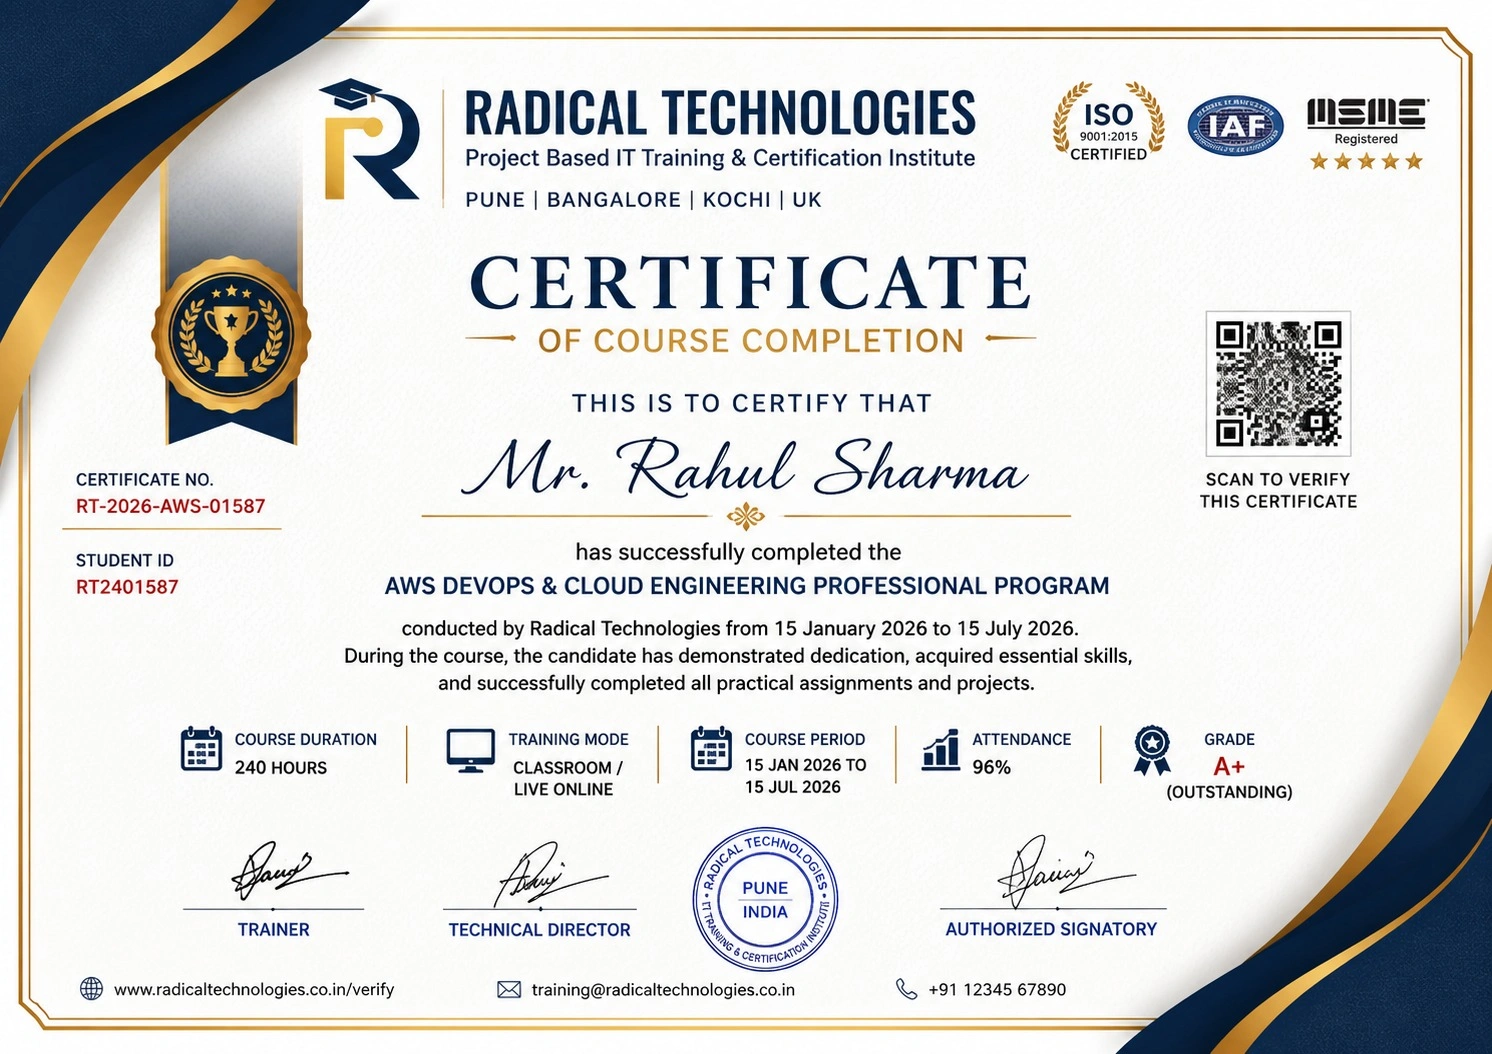
Certificate of Completion

Career Services

At Radical Technologies, we are committed to your success beyond the classroom. Our 100% Job Assistance program ensures that you are not only equipped with industry-relevant skills but also guided through the job placement process. With personalised resume building, interview preparation, and access to our extensive network of hiring partners, we help you take the next step confidently into your IT career.

Career Support

Course Completed? Need next steps?
Need Interview Supports?
Need Job Assistance?
Came from any other Institute?

Join our Brush-up Session & get support until you find a job!

Get Started

Radical Learning Eco-System

Exam Simulator

Cloud SandBox

Hands-on Cloud Lab

Developer Coding Ground

Student Reviews

4.7★
Average learner rating
50K+
Students trained
30+
Hiring companies alumni work at
100%
Placement assistance
4.7
★★★★★

Course Rating

★★★★★
79%
★★★★☆
16%
★★★☆☆
3%
★★☆☆☆
1%
★☆☆☆☆
1%
The AWS Certified Security – Specialty Course in Bengaluru offered by Radical Technologies was comprehensive and highly practical. It helped me gain in-depth knowledge of AWS security concepts.
S Satisfied Student
I highly recommend Radical Technologies for their AWS Certified Security – Specialty Classes in Bengaluru. The instructors were knowledgeable and provided hands-on experience with real-world scenarios.
S Satisfied Student
The AWS Certified Security – Specialty Certification in Bengaluru program at Radical Technologies gave me the confidence to handle security challenges on AWS. The training was exceptional!
S Satisfied Student
Radical Technologies is the best AWS Certified Security – Specialty Institute in Bengaluru for anyone looking to build a career in AWS security. Their teaching methods are top-notch.
S Satisfied Student
Enrolling in the AWS Certified Security – Specialty Training in Bengaluru at Radical Technologies was a game-changer for my career. The detailed course content and expert trainers made all the difference.
S Satisfied Student
I opted for the AWS Certified Security – Specialty Online Classes in Bengaluru, and the flexibility they offered was incredible. The live sessions and interactive learning experience were excellent!
S Satisfied Student
Radical Technologies’ AWS Certified Security – Specialty Online Training in Bengaluru was highly effective. The trainers ensured we understood every concept thoroughly with practical demonstrations.
S Satisfied Student
I completed the AWS Certified Security – Specialty Online Course in Bengaluru at Radical Technologies, and it exceeded my expectations. The study materials and support were exceptional.
S Satisfied Student
The AWS Certified Security – Specialty Corporate Training in Bengaluru offered by Radical Technologies was tailored to our team’s needs. It was an excellent investment for our organization.
S Satisfied Student
Radical Technologies provided me with the best AWS Certified Security – Specialty Certification in Bengaluru preparation. Their focus on practical knowledge made a huge difference.
S Satisfied Student
The AWS Certified Security – Specialty Course in Bengaluru at Radical Technologies was well-structured, and the trainers were highly skilled. It was a fantastic learning experience.
S Satisfied Student
I found Radical Technologies’ AWS Certified Security – Specialty Classes in Bengaluru to be incredibly informative and engaging. They prepared me thoroughly for the certification exam.
S Satisfied Student
Radical Technologies is undoubtedly the best AWS Certified Security – Specialty Institute in Bengaluru. Their in-depth training modules and real-time projects set them apart.
S Satisfied Student
I attended the AWS Certified Security – Specialty Training in Bengaluru, and it helped me advance my career significantly. The practical sessions were particularly helpful.
S Satisfied Student
The AWS Certified Security – Specialty Online Certification in Bengaluru program by Radical Technologies was extremely convenient and insightful. I’m now confident in my AWS security skills.
S Satisfied Student
The faculty at Radical Technologies made the AWS Certified Security – Specialty Online Classes in Bengaluru easy to follow. Their step-by-step approach to teaching was impressive.
S Satisfied Student
Completing the AWS Certified Security – Specialty Online Training in Bengaluru at Radical Technologies gave me the skills I needed to excel in AWS security roles. Highly recommend!
S Satisfied Student
Radical Technologies’ AWS Certified Security – Specialty Online Course in Bengaluru was a perfect fit for my schedule. The instructors were responsive and clarified every doubt.
S Satisfied Student
Our organization benefited greatly from Radical Technologies’ AWS Certified Security – Specialty Corporate Training in Bengaluru. The training improved our team’s understanding of cloud security.
S Satisfied Student
I chose Radical Technologies for the AWS Certified Security – Specialty Certification in Bengaluru, and I couldn’t be happier. The comprehensive training prepared me for the real-world challenges.
S Satisfied Student
Radical Technologies’ AWS Certified Security – Specialty Classes in Bengaluru were incredibly interactive. The trainers ensured that every student was on the same page.
S Satisfied Student
I am grateful for Radical Technologies’ AWS Certified Security – Specialty Course in Bengaluru. Their focus on hands-on training helped me secure a great job in cloud security.
S Satisfied Student
Radical Technologies’ AWS Certified Security – Specialty Online Certification in Bengaluru helped me achieve my goals. The course content was detailed and easy to understand.
S Satisfied Student
Attending the AWS Certified Security – Specialty Online Training in Bengaluru at Radical Technologies was a fantastic decision. The virtual sessions were as effective as in-person classes.
S Satisfied Student
The AWS Certified Security – Specialty Institute in Bengaluru, Radical Technologies, offers unparalleled training. Their curriculum is designed for both beginners and experienced professionals.
S Satisfied Student

Frequently Asked Questions

15 questions about the AWS Certified Security — Specialty course.

01 What is AWS Certified Security – Specialty?
AWS Certified Security – Specialty is a certification that validates advanced skills in securing data, applications, and workloads on AWS. It demonstrates proficiency in areas like encryption, identity management, monitoring, and compliance.
02 Who should take the AWS Certified Security – Specialty exam?
The exam is ideal for cloud security engineers, DevSecOps professionals, compliance managers, and IT administrators with experience in securing AWS environments and managing cloud risks.
03 What are the prerequisites for AWS Certified Security – Specialty?
While there are no formal prerequisites, AWS recommends at least 2 years of hands-on experience in securing AWS workloads and an understanding of AWS security services and best practices.
04 What topics are covered in the AWS Certified Security – Specialty exam?
The exam covers incident response, logging and monitoring, infrastructure security, identity and access management (IAM), data protection, and compliance.
05 How long is the AWS Certified Security – Specialty exam, and how is it structured?
The exam is 170 minutes long and consists of multiple-choice and multiple-response questions. It tests your knowledge of AWS security practices through scenario-based questions.
06 vWhat AWS services are essential for the AWS Certified Security – Specialty exam?
Key services include AWS Identity and Access Management (IAM), Amazon GuardDuty, AWS Security Hub, AWS WAF, AWS Shield, AWS KMS (Key Management Service), and AWS CloudTrail.
07 What is the passing score for the AWS Certified Security – Specialty exam?
The passing score is typically around 750 out of 1,000, but AWS does not publish an exact passing percentage. Performance across all exam domains is considered.
08 How much does the AWS Certified Security – Specialty exam cost?
The exam fee is $300 (USD), with additional costs for any practice exams or preparation courses. AWS occasionally offers promotional discounts or vouchers.
09 How can I prepare for the AWS Certified Security – Specialty exam?
Preparation options include studying AWS documentation, taking official AWS training courses, practicing hands-on with AWS services, and using practice exams to simulate the test environment.
10 How does AWS handle data encryption for security on its cloud platform?
AWS provides encryption services like AWS KMS, AWS Secrets Manager, and S3 bucket encryption to secure data at rest and in transit. These tools help meet industry compliance and security standards.
11 How does AWS Certified Security – Specialty help in career advancement?
This certification demonstrates expertise in AWS cloud security, opening opportunities for roles like Cloud Security Architect, DevSecOps Engineer, Compliance Manager, and Security Analyst.
12 What is AWS GuardDuty, and how is it relevant to the exam?
Amazon GuardDuty is a threat detection service that monitors AWS accounts for malicious or unauthorized activity. It’s an essential service for understanding AWS threat detection and incident response.
13 What are AWS WAF and AWS Shield, and why are they important?
AWS Web Application Firewall (WAF) protects web applications from common vulnerabilities, while AWS Shield defends against DDoS attacks. These services are critical for application and network security on AWS.
14 What compliance standards does AWS help businesses meet?
AWS offers services and documentation to help businesses comply with GDPR, HIPAA, PCI-DSS, ISO 27001, and other industry-specific regulations. AWS Artifact provides access to compliance reports.
15 How can AWS Certified Security – Specialty certification help businesses?
Businesses benefit by having certified professionals who can secure AWS environments, minimize risks, meet compliance requirements, and implement best practices for cloud security. This certification ensures robust protection of cloud assets.

AWS Certified Security — Specialty Interview Questions

10 questions commonly asked in AWS Certified Security — Specialty interviews.

  1. 01 How would you design a secure AWS environment for an organization with multiple accounts and varying levels of access?
  2. 02 What best practices would you follow to ensure data encryption at rest and in transit using AWS services?
  3. 03 Explain how AWS Security Hub can be used for centralized security monitoring across multiple AWS accounts and regions.
  4. 04 What steps would you take to implement the principle of least privilege using AWS Identity and Access Management (IAM)?
  5. 05 How do you configure AWS CloudTrail to ensure proper logging and monitoring of all account activities, and how would you secure these logs?
  6. 06 Describe how to handle a DDoS attack on an AWS-hosted web application using AWS Shield and AWS WAF.
  7. 07 How would you implement automated threat detection and response using Amazon GuardDuty and AWS Lambda?
  8. 08 What methods can be used to protect sensitive credentials and API keys within an AWS environment?
  9. 09 How would you approach securing serverless applications on AWS, particularly when using AWS Lambda and Amazon API Gateway?
  10. 10 Discuss your strategy for ensuring compliance with regulatory standards (e.g., GDPR, HIPAA, or PCI-DSS) in an AWS cloud environment.

The AWS Certified Security – Specialty Course Certification with Training in Pune

Radical Technologies is the leading institute in Bangalore for the AWS Certified Security – Specialty Course in Bengaluru, offering comprehensive training to help students and professionals build expertise in AWS cloud security. Our institute is renowned for its industry-oriented curriculum and hands-on learning approach, designed to provide in-depth knowledge of AWS security best practices.

As a top-rated AWS Certified Security – Specialty Institute in Bengaluru, we deliver structured AWS Certified Security – Specialty Classes in Bengaluru led by certified trainers with real-world experience. Our training includes detailed modules on identity and access management, data protection, incident response, monitoring, and compliance, ensuring students are well-prepared for both certification exams and real-world security challenges.

For professionals seeking flexible learning options, we provide AWS Certified Security – Specialty Online Classes in Bengaluru. These interactive sessions are designed to replicate the classroom experience, offering live demonstrations, practical exercises, and personalized mentorship. Our AWS Certified Security – Specialty Online Training in Bengaluru ensures that learners receive high-quality education from the comfort of their homes.

Radical Technologies also specializes in AWS Certified Security – Specialty Corporate Training in Bengaluru, tailored to meet the unique needs of businesses looking to upskill their teams. We focus on practical, role-based training to empower corporate teams with AWS security knowledge and compliance practices.

Whether you’re preparing for the AWS Certified Security – Specialty Certification in Bengaluru or looking to enhance your AWS security skills, Radical Technologies is your one-stop destination. Enroll in our AWS Certified Security – Specialty Online Course in Bengaluru today and take the first step towards securing your future in AWS cloud security!

Our Alumni Work At
Accenture
Amazon
Avisys Services
Birlasoft
Capgemini
Catchpoint
Cognizant
Darwish Cybertech
DataVision
GiBots
Google
Groots Software
HCL Technologies
IBM
Info Gain
Infosys
ITCube Solutions
KPIT
L&T Infotech
Microsoft
Mphasis
mPhatek
Oracle
Quantbit Technologies
Saina Cloud
TCS
Tech Mahindra
Wipro
YASH Technologies
Zensar Technologies
Accenture
Amazon
Avisys Services
Birlasoft
Capgemini
Catchpoint
Cognizant
Darwish Cybertech
DataVision
GiBots
Google
Groots Software
HCL Technologies
IBM
Info Gain
Infosys
ITCube Solutions
KPIT
L&T Infotech
Microsoft
Mphasis
mPhatek
Oracle
Quantbit Technologies
Saina Cloud
TCS
Tech Mahindra
Wipro
YASH Technologies
Zensar Technologies

Get a Call Back from Our Career Assistance Team

Request Callback